Table of Content
- Why Employees Become Targets During Reconnaissance
- The Information Attackers Try to Connect
- From Public Information to Social Engineering
- Why Identity Management Matters Before an Attack Happens
- Reducing the Value of Employee Reconnaissance
- Building a Culture That Makes Reconnaissance Less Useful
- Reconnaissance Is a Warning, Not an Inevitable Breach
- Conclusion
A cyberattack rarely begins with someone suddenly breaking through a company's strongest technical defenses. In many cases, the groundwork starts much earlier, with an attacker quietly learning about the people behind the organization. Names, job titles, reporting relationships, email formats, public profiles, company announcements, professional achievements, and even casual social media posts can collectively reveal enough information to make a later attack more convincing. The employee becomes the map, and the organization becomes the destination.
This type of preparation is commonly described as reconnaissance, and it is an important part of modern social engineering and identity-based attacks. Attackers are not necessarily looking for one spectacular piece of information. They are assembling small details into a useful picture of how an organization operates. Once they understand who has authority, who handles payments, who works in IT, who recently joined the company, and which employees interact with external partners, they can create highly targeted attempts that appear legitimate.
Why Employees Become Targets During Reconnaissance
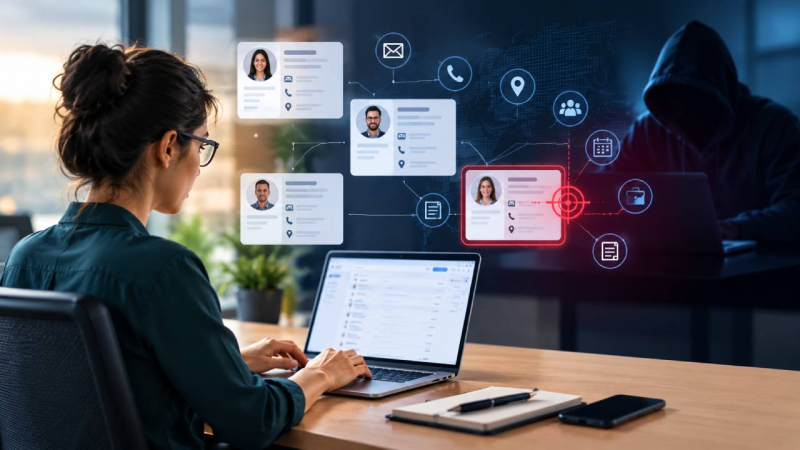
Organizations naturally publish information about their people. Company websites introduce executives and department leaders. Professional networks reveal career histories and responsibilities. Press releases announce promotions, acquisitions, conferences, and new projects. Job advertisements describe technologies and internal functions. Social media can add even more context, sometimes including information employees never intended to provide to an unknown audience. Individually, these details may seem harmless. Together, they can provide a surprisingly detailed picture of an organization's human structure.
Attackers can use this information to identify individuals whose roles may provide valuable access. An accounts-payable employee, for example, may regularly handle invoices and banking information. An IT administrator may have privileged access to systems. An executive assistant may coordinate sensitive schedules and communications. A newly hired employee may still be learning internal procedures. Understanding these distinctions helps an attacker choose an appropriate pretext rather than sending the same generic message to everyone.
The emphasis on people is consistent with broader identity-security guidance. CISA has highlighted legitimate user access, compromised credentials, social engineering, phishing, and alternative access paths among the threats organizations need to address. NIST's current digital identity guidance likewise recognizes impersonation and social engineering as important threats to identity processes. The lesson is straightforward: protecting infrastructure without considering how attackers understand and manipulate users leaves an important part of the attack surface exposed.
The Information Attackers Try to Connect
Reconnaissance becomes particularly useful when isolated pieces of information can be connected. Knowing that someone works for a particular company is relatively unremarkable. Knowing that the same person is a recently promoted finance manager, reports to a specific executive, uses a particular business email format, and is attending an industry conference creates a much more useful profile.
Organizational relationships can be especially valuable. Publicly available information may reveal who reports to whom, which teams collaborate, which employees communicate with customers, and which executives approve important decisions. Attackers can then construct messages that exploit those relationships. A fraudulent request from a supposed manager can seem more believable when the attacker understands the company's hierarchy and uses familiar terminology.
Timing can make reconnaissance even more effective. A company announcing an acquisition, moving offices, launching a product, changing leadership, or recruiting for a new department may inadvertently provide clues about what employees are currently focused on. A convincing malicious message can be built around those events. This is one reason cybersecurity awareness cannot be treated solely as an annual training exercise. Employees need practical guidance for recognizing unusual requests in the context of their everyday work.
From Public Information to Social Engineering
The ultimate purpose of reconnaissance is often not information collection for its own sake. It is preparation for persuasion. Social engineering depends on creating a believable situation that encourages a person to reveal information, approve an action, open a malicious file, transfer money, or authenticate to a fraudulent service.
A well-researched message can be significantly more convincing than an obviously generic phishing email. Instead of saying, "Your account has a problem," an attacker may reference a real department, a legitimate project, a known colleague, or a current business event. The goal is to reduce suspicion by making the communication fit naturally into the employee's expectations. NIST specifically identifies social engineering as a threat in which an attacker attempts to persuade a legitimate person to take an action that ultimately enables account or identity compromise.
This is also why employees should not be blamed when sophisticated deception succeeds. Security is a shared responsibility, and technical controls should assume that convincing messages will occasionally reach legitimate users. CISA recommends multifactor authentication because passwords alone are insufficient protection against account compromise, while stronger phishing-resistant authentication can provide additional protection. Good security therefore combines employee awareness with controls that reduce the consequences of a successful deception.
Why Identity Management Matters Before an Attack Happens
Traditional security programs often focus heavily on what happens after someone attempts to access a system. Reconnaissance suggests that organizations should also consider the information available before that access attempt occurs. If attackers can easily determine which external identities have access to company resources, which accounts belong to former employees, and which partners have privileged permissions, they have more opportunities to identify weaknesses.
This is where external identity management can become part of a broader identity-security strategy. Organizations increasingly work with contractors, vendors, consultants, partners, customers, and other outside users who may require access to selected systems. Managing these identities carefully can help organizations understand who has access, why they have it, and whether that access remains appropriate as relationships change.
Current NIST guidance emphasizes identity proofing, authentication, federation, and ongoing digital identity risk management. Its risk-management framework specifically considers the consequences of an attacker impersonating a legitimate user, compromising authentication, or gaining access through federated identity mechanisms. CISA guidance similarly calls attention to risks involving former employees, external accounts, legitimate users, authentication assertions, and alternative access points. Effective identity management therefore has a role beyond convenience. It helps establish clearer boundaries around who should be trusted with organizational resources.
Reducing the Value of Employee Reconnaissance
Organizations cannot realistically remove every piece of information about their employees from the internet. They can, however, become more deliberate about what they publish and how that information can be combined. Public-facing employee directories should contain only information that serves a legitimate business purpose. Job descriptions can explain responsibilities without unnecessarily revealing sensitive technical architecture. Employees can also review their professional and social profiles to identify details that could make impersonation easier.
Internal processes matter just as much. Employees should know how to verify unusual requests, particularly those involving payments, credentials, access changes, confidential information, or urgent executive instructions. Verification should happen through a trusted communication channel rather than simply replying to the suspicious message. A request that appears to come from a senior executive may still deserve independent confirmation when it involves an unusual action.
Technical controls provide another layer of protection. Strong authentication, appropriate access permissions, account lifecycle management, logging, and timely removal of unnecessary access can limit what happens if an attacker successfully obtains credentials. NIST's latest digital identity framework emphasizes risk-based controls and continuous evaluation rather than treating identity security as a one-time implementation. This approach recognizes that employee roles, technology environments, external relationships, and threats change over time.
Building a Culture That Makes Reconnaissance Less Useful
Security awareness is most effective when employees understand the reasoning behind the rules. Telling someone simply not to click suspicious links is less useful than explaining how an attacker might have learned their name, role, manager, or current project. When people understand the reconnaissance stage, unusual familiarity becomes a warning sign rather than a source of reassurance.
Organizations can reinforce this mindset through realistic exercises and clear reporting procedures. Employees should know where to report suspicious emails, unexpected authentication prompts, unusual requests from executives, or messages involving unfamiliar external contacts. Reporting should be encouraged rather than treated as an admission of failure. Early reporting can allow security teams to investigate before a minor interaction becomes a larger incident.
The strongest culture also avoids treating identity security as solely an IT responsibility. Human resources, finance, management, communications, procurement, legal teams, and individual employees all influence the amount of information an organization exposes and the access that different people receive. Identity security becomes more resilient when these functions work together and when access is regularly reviewed according to actual business needs.
Reconnaissance Is a Warning, Not an Inevitable Breach
Attackers may be able to discover information about an organization and its employees, but reconnaissance does not automatically lead to a successful compromise. The important question is how much value that information provides once an attacker tries to use it. Strong authentication, sensible access controls, verification procedures, employee awareness, and careful identity lifecycle management can make stolen context considerably less useful.
The modern security environment makes this layered approach increasingly important. NIST's 2025 Digital Identity Guidelines address identity proofing, authentication, federation, and identity risk management, reflecting the central role that digital identity now plays in protecting online services. CISA likewise emphasizes layered identity and access management practices rather than relying on a single defensive measure.
Conclusion
The first stage of an attack may happen long before a malicious file is opened or a password is entered. It can begin with an attacker simply learning who works at an organization, what those people do, who they report to, and which relationships might be trusted. Recognizing this reality changes the way businesses think about security. Employees are not merely potential victims sitting behind protected systems. They are part of the organization's identity and access environment.
The goal is not to hide every employee from the public or make ordinary business communication impossible. It is to reduce unnecessary exposure, strengthen verification habits, manage internal and external identities carefully, and build technical safeguards that limit the impact of mistakes. When reconnaissance produces less useful information, and compromised credentials provide less opportunity, attackers have a much harder path from observation to intrusion. A security-conscious organization does not assume that its people will never be targeted. It prepares so that being targeted does not automatically mean being compromised.
Post Comment
Share your thoughts about this article.
Be the first to post a comment!